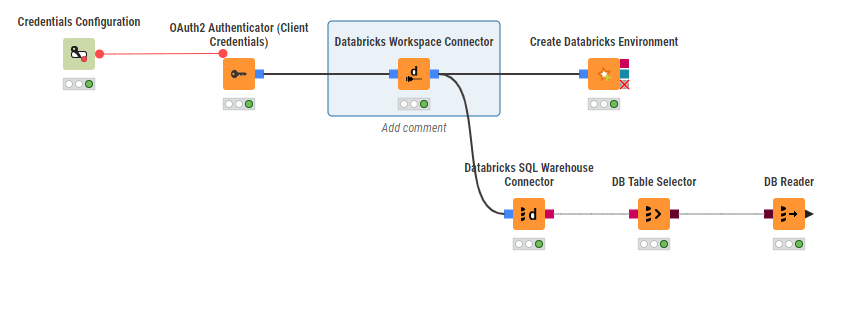
I know PAT is the preferred auth method for creating a Databricks environment, but my work is moving away from those and will no longer allow developers to generate them.
Is there a way I can authenticate with a Databricks Managed Service Principal instead? Or is this simply not possible?
I am using version 5.4.4
Hi @Gordon111,
Welcome to the Forum!
Yes, you can connect to Databricks using a Service Principal via the OAuth2 Authenticator (Client Credentials) node in KNIME.
In the configuration, fill in the following:
- Token endpoint:
https://<your-workspace>.cloud.databricks.com/oidc/v1/token
- ID and Secret (flow variable): Provided via a flow variable from the Credentials Configuration node (Client ID and Secret of your service principal)
- Scope:
all-apis
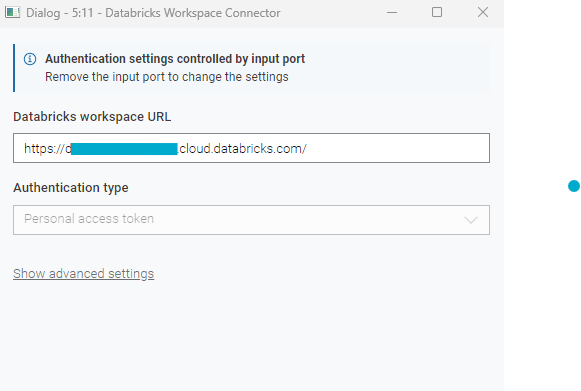
Once configured, connect the OAuth2 Authenticator to the Databricks Workspace Connector, set your workspace URL there, and then continue to the Create Databricks Environment node.
Best,
Keerthan